
What does the EU AI Act mean for a business?
The Regulation follows a risk-based approach. Different systems and uses may trigger different obligations, while some practices are prohibited and some systems are subject mainly to transparency requirements.
The relevant question is not simply whether a company uses AI. It is what the system does, where it is used, who provides or deploys it and how it may affect people or decisions.
First step: know which AI systems the organisation uses
A company cannot classify or govern systems it has not identified. An initial inventory should include tools developed internally, systems purchased from providers, AI embedded in other software, pilot projects and relevant informal uses by teams.
The first version does not need dozens of fields. Record the system, its purpose, owner, provider, data, affected people and role in decision-making. That is enough to begin prioritising.
Provider or deployer: what role does your business play?
Obligations depend partly on the organisation’s role. A provider develops an AI system or has it developed and places it on the market or puts it into service under its name. A deployer uses an AI system under its authority, except for personal non-professional activity.
Many companies will mainly be deployers, but roles can change when a system is substantially modified, rebranded or developed for others. The answer should be documented rather than assumed.
How to classify AI systems under the AI Act
A practical order is to check prohibited practices first, then potential high-risk systems under Article 6 and Annexes I and III, then transparency obligations and, finally, other governance or contractual needs.
Classification must be based on the actual intended purpose and use of the system, not only on a supplier’s marketing description.
Prohibited practices: what should we check first?
Some AI practices are prohibited because the Regulation considers their risk unacceptable. A company should check early whether any current or planned use could fall within Article 5.
This review must be specific. Broad labels such as ‘chatbot’ or ‘analytics’ are not enough to determine whether a practice is prohibited.
High-risk AI systems: when closer attention is needed
High-risk systems may arise because they are safety components of regulated products or because they perform sensitive functions listed in Annex III, including certain uses in employment, education, essential services and law enforcement.
Being connected to an Annex III area does not always end the analysis. The function, influence on decisions, possible Article 6(3) exceptions and any profiling of natural persons must also be checked.
Transparency and AI literacy: obligations that already matter
Not every relevant obligation is limited to high-risk systems. Organisations should review transparency duties for certain systems and ensure an appropriate level of AI literacy among staff and others dealing with AI on their behalf.
Training should relate to people’s roles, the systems they use and the risks they may encounter. A generic presentation is not always enough.
A straightforward route to start complying
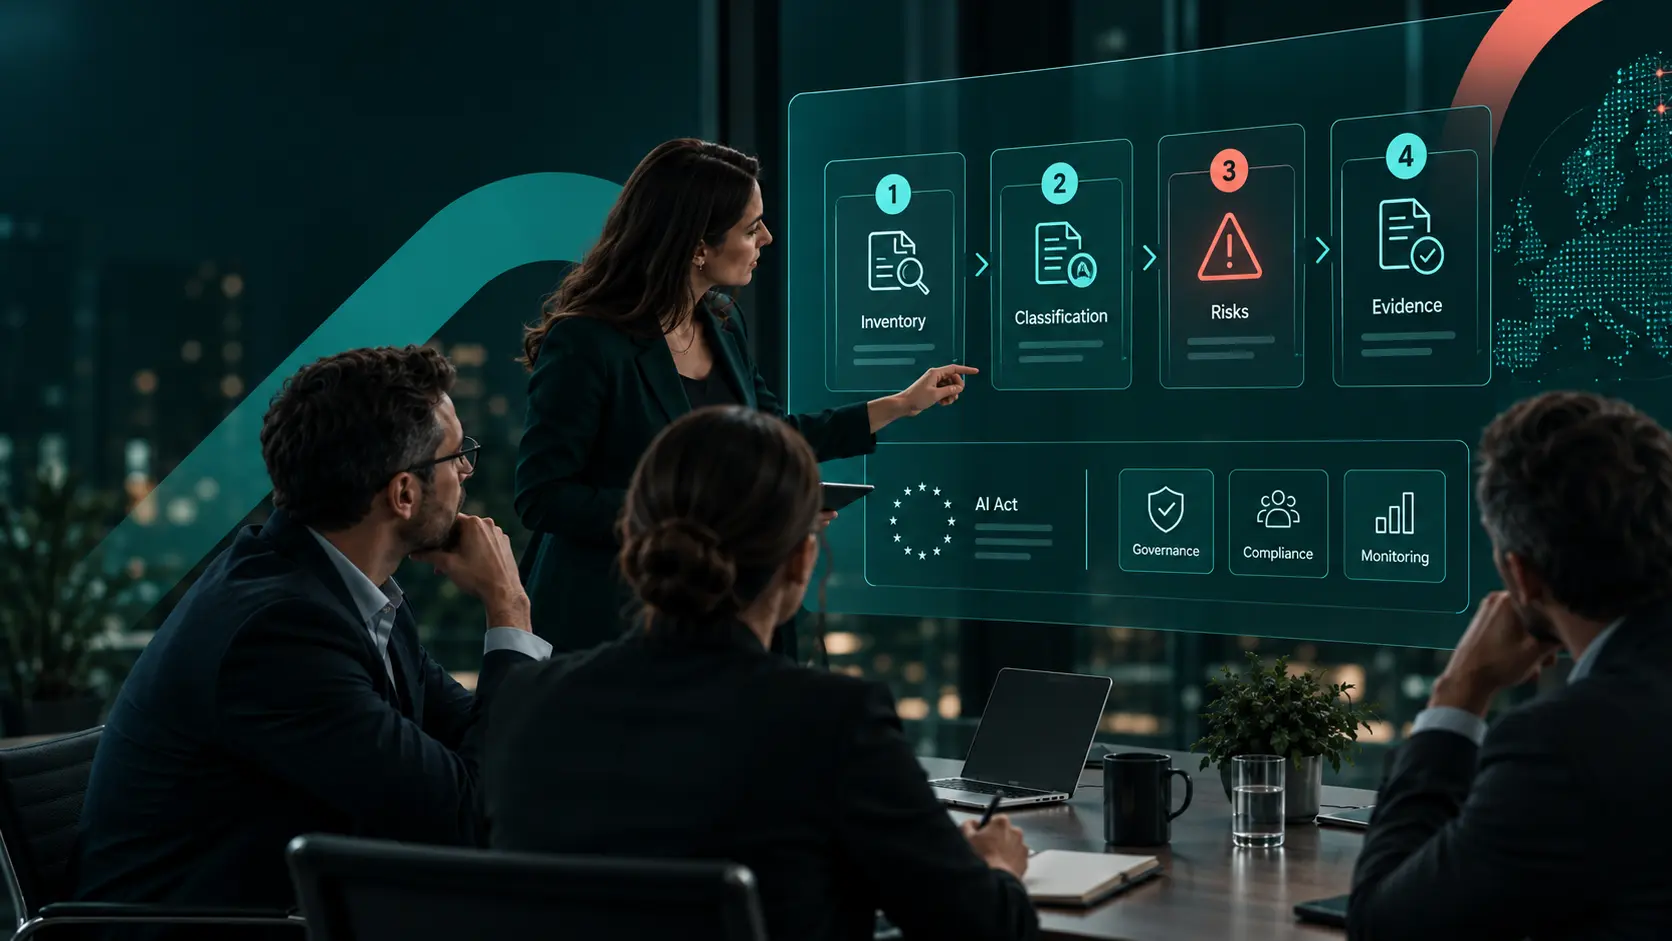
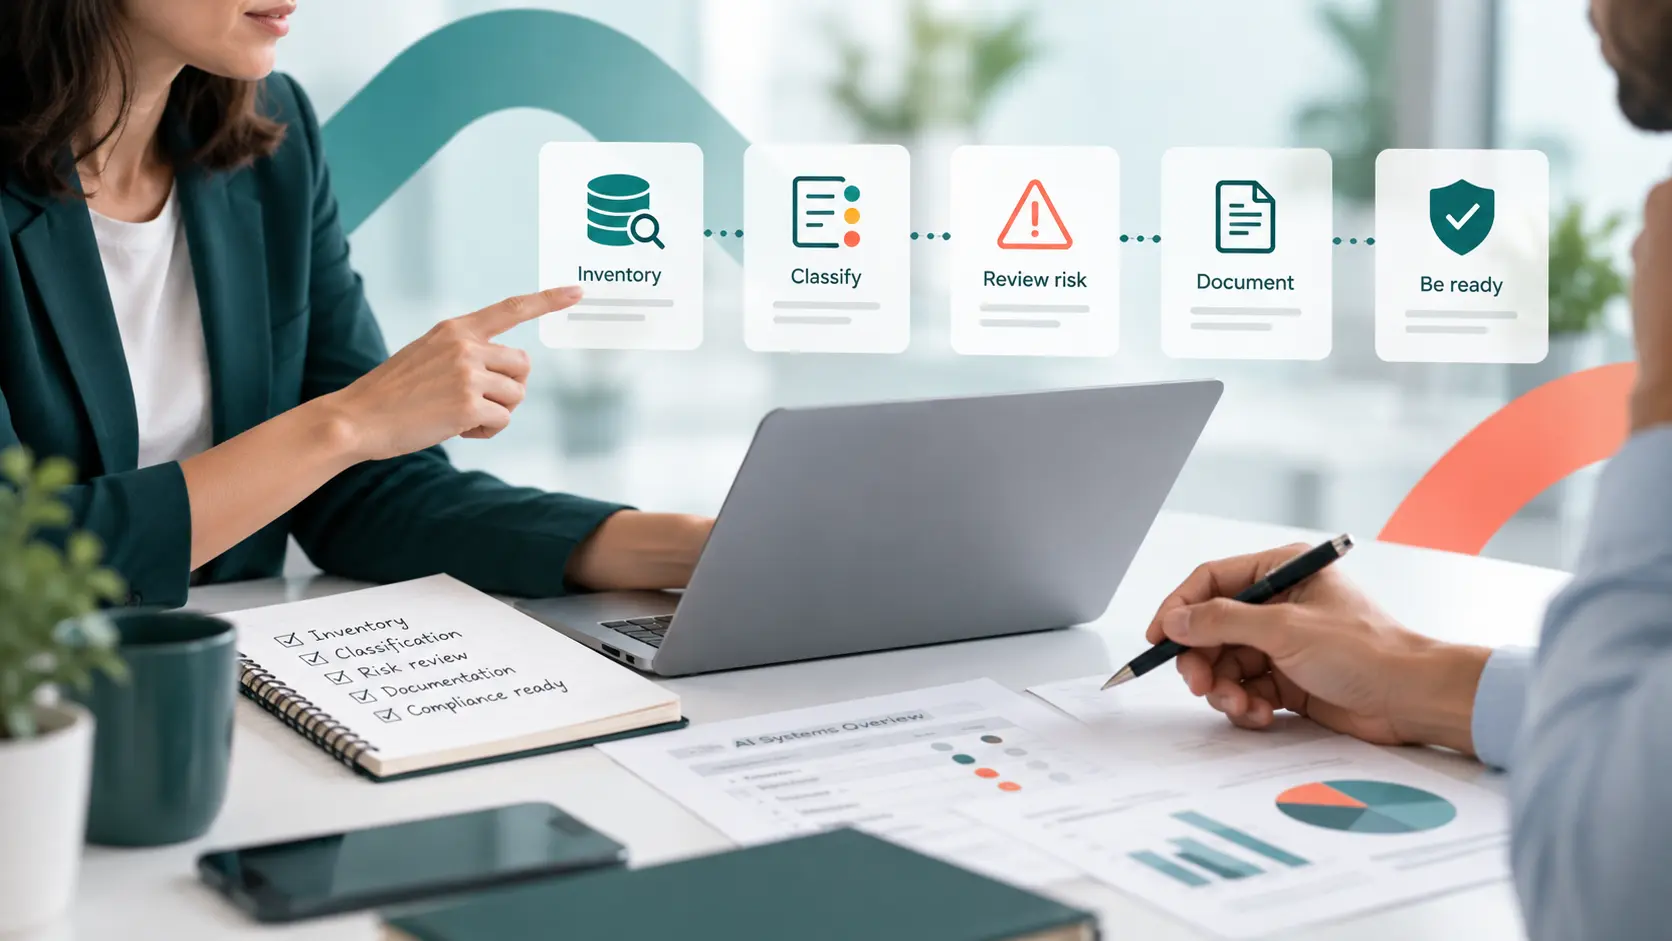
A manageable first route is to create the inventory, assign owners, describe intended uses, perform an initial classification, identify applicable obligations, prioritise higher-impact systems and preserve the evidence behind each decision.
This turns the AI Act from an abstract legal text into a set of specific actions connected to real systems.
Common mistakes when approaching compliance
Frequent mistakes include starting with policies before knowing which systems exist, relying entirely on supplier statements, treating all AI in the same way, ignoring informal use, confusing technology with risk and failing to record the reasoning behind decisions.
Another mistake is waiting for every detail to be perfect. A controlled first version that can be improved is usually more useful than an ambitious programme that never becomes operational.
What should a business have after this first review?
After the first phase, the organisation should have a usable inventory, identified owners, an initial classification, a list of priority systems, a view of applicable obligations and a record of the information and decisions used.
It will not mean that all compliance work is complete. It will mean the company finally has a reliable starting point.
Which AI Act obligations already apply in 2026?
The AI Act applies in stages. Prohibited practices and AI literacy provisions began applying before the full framework, while other requirements follow the Regulation’s timetable.
Because dates and guidance may evolve, organisations should keep their implementation plan under review and verify the rules applicable to each system and role at the relevant time.
Where should your business begin?
Begin with visibility. Identify the systems, their uses and their owners before producing large volumes of documentation.
Start the Céntrika assessment →
Use the Céntrika assessment to obtain an initial view of your organisation’s AI governance, risk and compliance.
The assessment provides initial guidance and does not replace a specific legal or technical evaluation.