
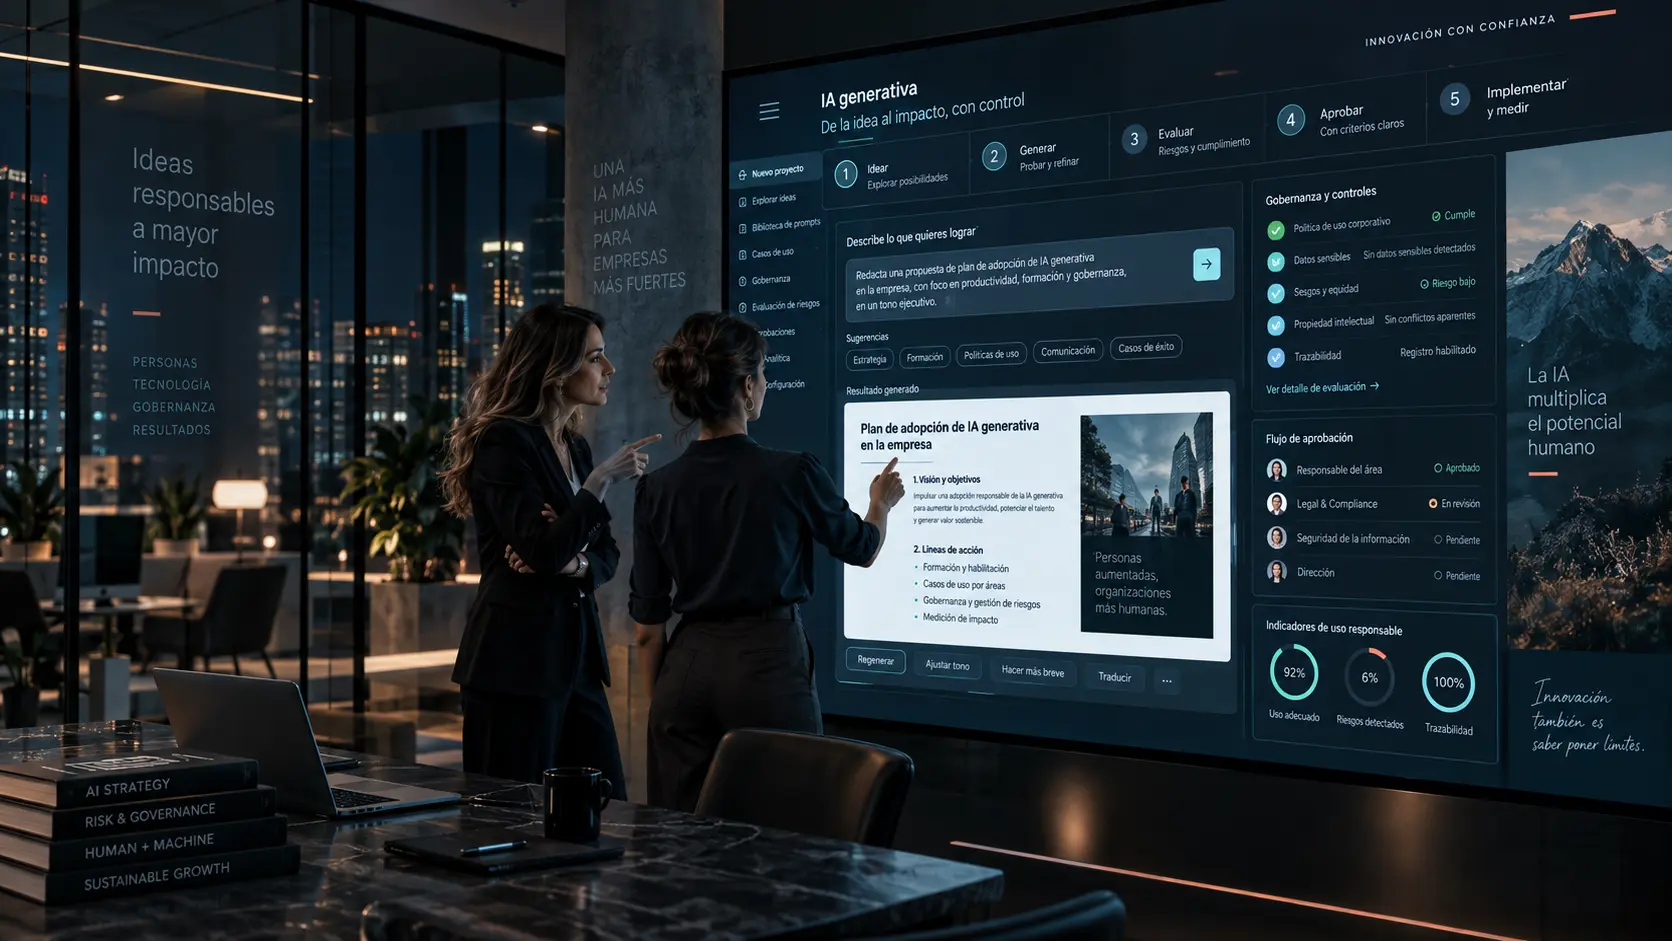
Why generative AI needs governance
Generative AI dramatically lowers the barrier to entry. A browser and an account may be enough. Adoption can be rapid, but the organisation can lose visibility of tools, purposes, data, outputs, vendors and risk.
Governance should ask not “do we allow generative AI?” but “which uses are we prepared to allow, and under what conditions?”
The first risk: not knowing who uses it
Ungoverned adoption creates shadow AI: tools used without approval, through personal accounts, without understanding the terms or while entering information that should not be shared.
This often happens because the organisation has not approved tools, communicated practical rules, provided alternatives or made timely decisions.
The AI inventory and AI use policy must work in practice. A simple ban may push use outside organisational control.
Start with use cases
Low-impact use
- ideas, drafts, rewording, preliminary translation and brainstorming.
Use requiring review
- external documents, proposals, analysis, customer content and code.
Sensitive use
- decisions about people, specialist advice, regulated information and critical processes.
This classification enables proportionate controls linked to AI risk management.
Approved, restricted and unauthorised tools
An acceptable-use model can distinguish approved tools, tools allowed only with particular accounts or settings, restricted uses requiring approval, and unauthorised tools or uses.
Employees receive a practical answer: “I can use this tool for this task.”
What data can be entered
Prompts may contain personal data, trade secrets, contractual or customer information, code and internal documents.
Rules should distinguish public, internal, confidential and particularly sensitive information. Internal information may require corporate tools; confidential information may be restricted; sensitive data may need additional controls.
Intellectual property and generated content
Generative AI raises questions about intellectual property, third-party rights, reuse, attribution, derivative content and licensing.
Define which outputs may be published, when review is needed, which checks apply and when legal input is required.
Errors, hallucinations and bias
A convincing output can still be wrong. AI may invent facts, cite non-existent sources, oversimplify, reproduce bias, lose context or produce inconsistent results.
The greater the potential impact, the stronger the human verification should be.
Human review and accountability
Generative AI can support decisions but should not automatically become the decision-maker.
Define which outputs need review, who reviews them, what must be checked, who approves and who remains accountable.
“The AI said so” does not transfer responsibility. Human oversight should be genuine and proportionate.
Vendors, models and external tools
Commercial tools may involve an application vendor, model provider, cloud supplier and integrations. Understand who processes data, which model is used, whether prompts are retained or used for training and what may change.
Using a commercial tool built on a general-purpose AI model does not automatically make the user organisation the legal provider of that model. Governance also requires AI vendor management.
How to design a generative AI governance model
Step 1. Identify uses and categories
Understand who uses generative AI, for what purpose and at what level of risk.
Step 2. Approve tools and data rules
Specify which solutions and information may be used.
Step 3. Define human review
Determine which outputs need validation.
Step 4. Build capability
Explain risk, limitations, policy and escalation through AI literacy.
Step 5. Integrate vendors and evidence
Assess external tools and record significant decisions.
Step 6. Monitor and review
Detect incidents, shadow AI and new uses, and update the model as tools and risk change.
The aim is controlled enablement, not prohibition by default.
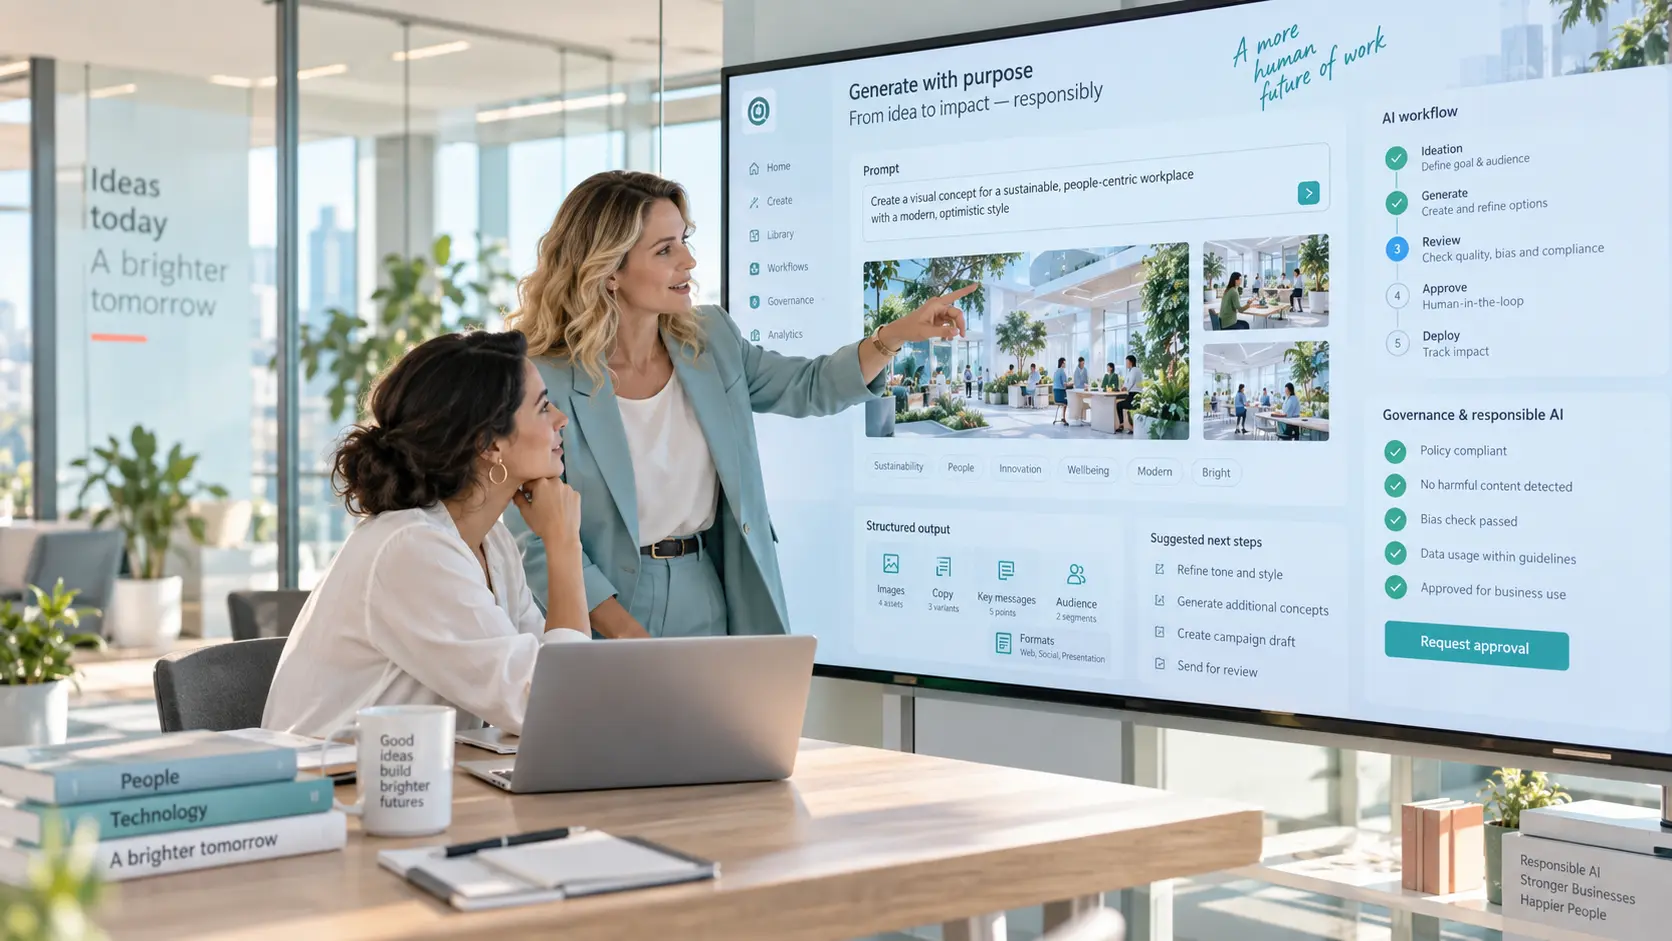
Transparency and AI-generated content
The AI Act contains contextual transparency duties for certain systems and AI-generated or manipulated content. Article 50 applies from 2 August 2026.
In specified circumstances, providers of systems that generate synthetic audio, image, video or text must ensure outputs are marked in a machine-readable format and detectable as artificially generated or manipulated.
Specific duties also apply to certain deepfakes and certain text published to inform the public on matters of public interest.
This does not mean every item of internal AI-generated content must automatically carry a visible label. The duty depends on content type, purpose, role and context.
Internal policy should distinguish internal use from external or public content, but it does not replace legal analysis or the relevant AI Act obligations.
Evidence and traceability
Not every prompt needs to be logged. Some activities may require evidence: the approved tool, risk assessment, vendor review, training, policy, sensitive-use approval, incidents and reviews.
For higher-impact uses, it may be reasonable to retain the version, output, human review and final decision. Traceability should be proportionate and can use a practical AI register.
How to measure whether the model works
Measures may include approved tools, trained users, registered cases, incidents, detected shadow AI, rejected outputs, completed reviews, questions and vendors assessed.
The purpose of governance is not to reduce AI use. It is to increase responsible adoption.
Common mistakes
Banning everything
Use often moves outside organisational control.
Allowing everything
Common criteria disappear.
Writing an excessively long policy
People need clear rules.
Focusing only on prompts
Governance also covers vendors, data, risk and decisions.
Treating every use in the same way
An internal draft and a decision about a person do not carry the same risk.
Failing to train or review vendors
Policy has little effect without understanding, and tools change quickly.
What an organisation should do now
1. Identify tools and uses
Establish what is used and why.
2. Classify uses and approve tools
Group uses by contextual impact and create a clear approved list.
3. Define data and review rules
State what may be entered and which outputs require validation.
4. Train, monitor and update
Explain the rules, detect incidents and new uses, and keep the model current.
The final question is: “can we enable people to use generative AI without losing control of the risks it introduces?”
Governing generative AI does not mean holding it back
The choice is not between innovation and control. An organisation can have both by connecting tools, people, data, risk, vendors, human review and evidence.
Good governance does not require permission for every prompt. It defines what people may do freely, what requires caution and what needs an additional decision.
When the rules are clear, governance enables safer and more useful AI through an AI governance framework.
References
- Regulation (EU) 2024/1689 — Artificial Intelligence Act.
- Article 4 — AI literacy.
- Article 50 — Transparency obligations.
- Articles 53 and 55 — Obligations for providers of general-purpose AI models.
- European Commission — Guidelines on transparency obligations under Article 50.
- European Commission — Code of Practice on Transparency of AI-generated Content.
- ISO/IEC 42001:2023 — Artificial intelligence management system.
- ISO/IEC 23894:2023 — Guidance on AI-related risk management.
Do you know how generative AI is being used in your organisation?
The first step is not to ban it. It is to understand which tools are being used, who uses them, what data they handle and what risks they create.
Start the diagnostic →
Céntrika’s diagnostic can help identify that starting point.