
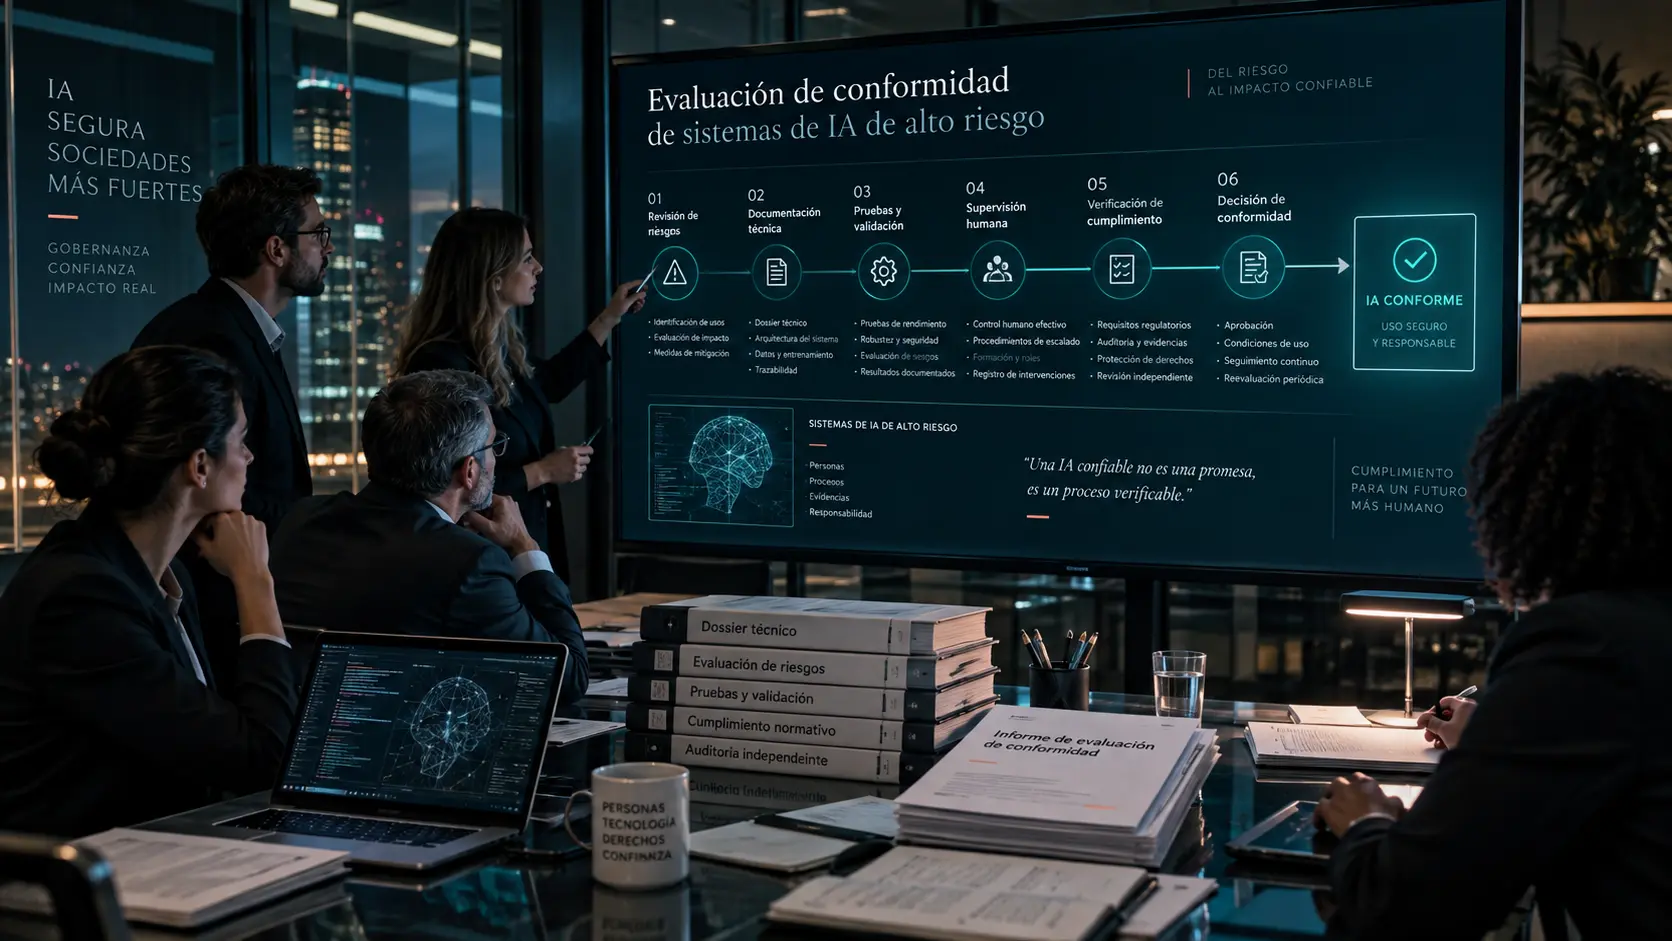
What a conformity assessment is
Conformity assessment is the process used to determine whether a high-risk AI system meets applicable requirements.
It is not simply an audit, certification or document review. It may combine technical documentation, controls, testing, risk management, a quality management system, internal review and, where required, a notified body.
Which systems must undergo it
High-risk systems must follow the relevant route before being placed on the market or put into service.
Routes differ between Annex III systems and systems embedded in products regulated under Annex I legislation. Correct AI Act classification therefore comes first.
What requirements are assessed
The assessment covers applicable Chapter III, Section 2 requirements, including risk management, data governance, technical documentation, record-keeping, transparency, human oversight, accuracy, robustness and cybersecurity.
Conformity depends on a complete system of controls and evidence, not one document.
The difference between Annex VI and Annex VII
Annex VI
Internal control: the provider assesses conformity internally and no notified body participates.
Annex VII
Assessment based on the quality management system and technical documentation, with a notified body.
They are different procedures, not interchangeable labels.
When internal control can be used
Article 43 provides internal control under Annex VI for certain Annex III systems. In particular, systems listed in points 2 to 8 currently follow this route without a notified body.
Internal control is not an unsupported self-declaration. The provider must demonstrate compliance through controls, results and AI evidence.
When a notified body is involved
Annex VII may apply in specified cases concerning point 1 of Annex III.
It also applies in Article 43 circumstances involving unavailable harmonised standards or common specifications, standards that are not applied or only partly applied, unapplied common specifications, or relevant restrictions on a published standard.
The notified body reviews the quality management system, technical documentation and applicable requirements. Not every high-risk system requires one.
AI systems linked to regulated products
Where a high-risk AI system forms part of a product covered by Annex I Union harmonisation legislation, the provider follows the applicable sectoral conformity procedure and integrates AI Act requirements into it.
A needless parallel process should not be created.
How the assessment works step by step
Step 1. Classify the system
Confirm that it is high-risk.
Step 2. Determine the route
Choose Annex VI, Annex VII or the Annex I sectoral procedure.
Step 3. Identify requirements
Define what must be demonstrated.
Step 4. Prepare technical documentation
Consolidate architecture, purpose, data, risk, testing and controls in the technical file.
Step 5. Review the management system
Assess the quality management system where relevant.
Step 6. Perform testing
Verify accuracy, robustness, security, operation and controls.
Step 7. Review evidence
Ensure each requirement can be demonstrated.
Step 8. Involve a notified body
Do so only when the procedure requires it.
Step 9. Resolve non-conformities
Close identified gaps.
Step 10. Complete the assessment
Formalise the outcome.
Step 11. Complete subsequent obligations
Where applicable, prepare the EU declaration of conformity, CE marking and registration.
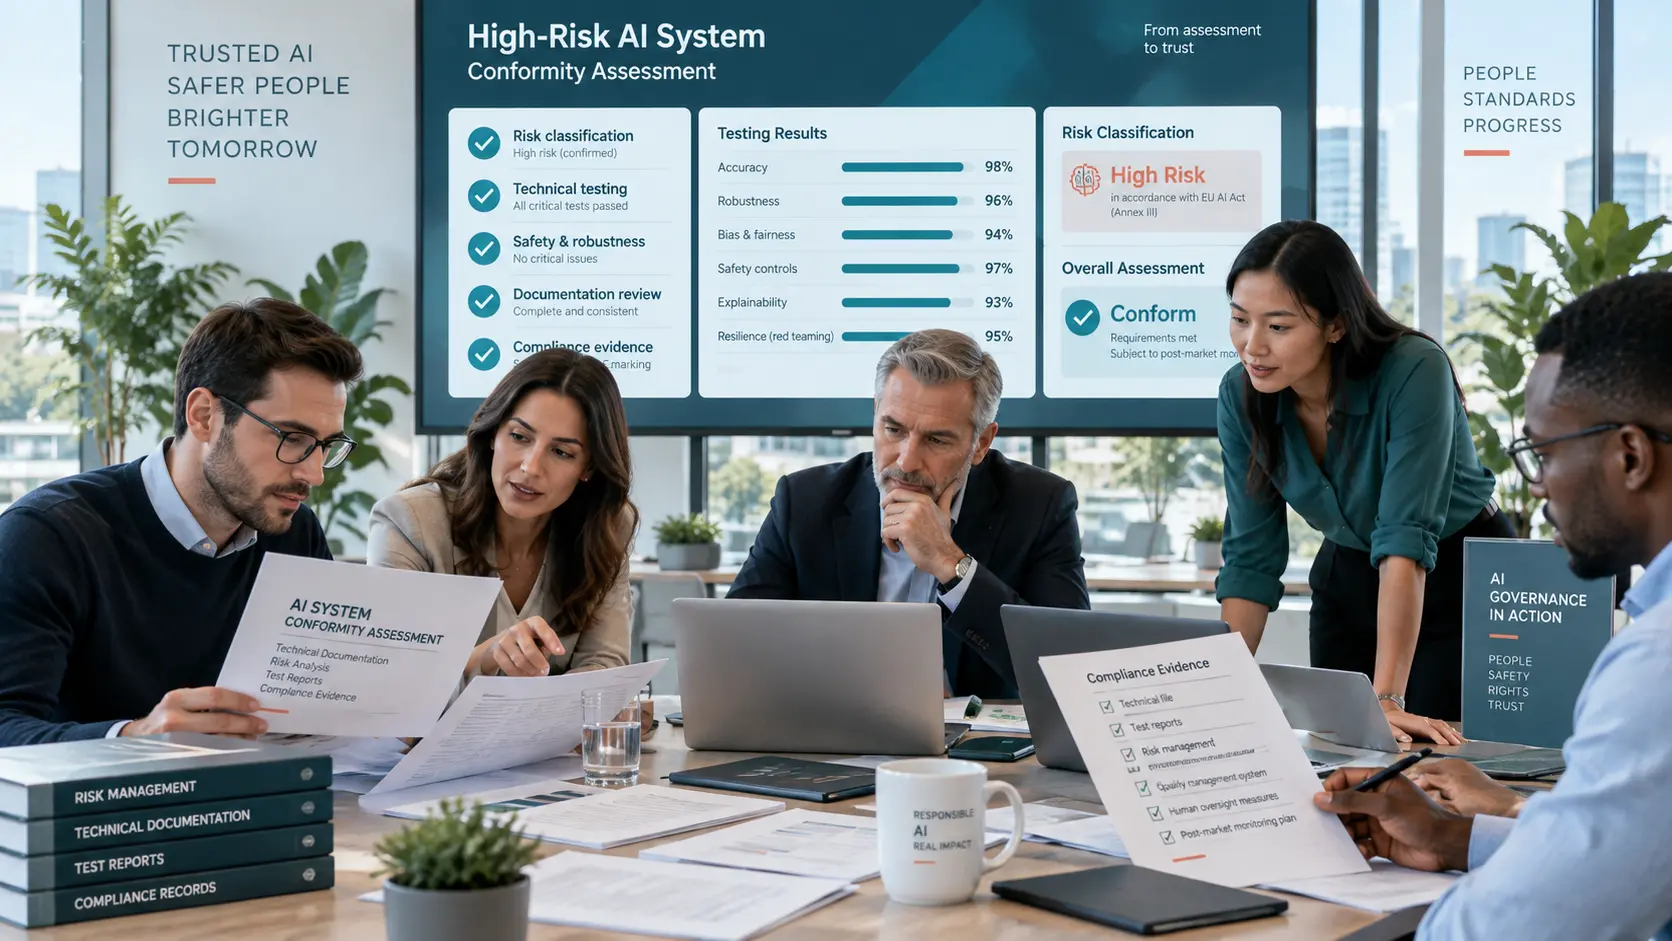
Technical documentation
The technical documentation should show how the system was designed, developed, tested and controlled, including purpose, architecture, data, tests, risk, controls, oversight, logs and changes.
It must be complete, coherent, current and traceable.
Quality management system
Article 17 requires providers of high-risk systems to maintain a quality management system covering compliance strategy, design, development, testing, validation, data, risk management, monitoring, incidents, documentation and responsibilities.
Under Annex VII, it forms part of the notified body assessment.
Risk, data, logs and human oversight
These elements should connect as risk → control → test → log → oversight → evidence.
The assessment should show that risks are identified, data governed, controls effective, traceability available, human oversight genuine, and required accuracy, robustness and cybersecurity achieved.
What happens after the assessment
Passing the assessment does not end the work. Providers must monitor, manage incidents, maintain documentation, update records, review risk and control change.
Conformity is part of the lifecycle and the wider AI governance framework.
What happens when the system changes
Article 43 requires a new assessment after a substantial modification, whether the modified system is redistributed or remains in use by the current deployer.
For continuously learning systems, changes predetermined by the provider and assessed during the original assessment may not constitute a substantial modification.
This makes AI system change management essential.
The relationship with CE marking and registration
Once conformity is demonstrated, the EU declaration of conformity, CE marking and registration may follow where applicable.
They do not replace the assessment. CE marking is not a standalone certification detached from the process.
Common mistakes
Assuming every system needs a notified body
That is incorrect.
Treating internal control as no control
It still requires evidence.
Choosing Annex VI or VII before classification
The system type must come first.
Treating the process as an ISO audit
They are not equivalent, and ISO/IEC 42001 does not replace Article 43.
Preparing documentation at the end
Evidence should follow the lifecycle.
Ignoring sectoral legislation
An integrated procedure may apply.
Failing to manage change
A substantial modification may trigger reassessment.
Confusing CE marking with assessment
The marking follows the relevant process.
Conformity is not demonstrated by one audit
Assessment connects classification → requirements → controls → evidence → assessment → market placement.
The route may vary, but the central question remains: can the provider demonstrate that the system meets the requirements that apply to it?
That requires coherence across risk, data, controls, tests, people and evidence.
References
- Regulation (EU) 2024/1689 — Artificial Intelligence Act.
- Article 16 — Obligations of providers of high-risk AI systems.
- Article 17 — Quality management system.
- Article 43 — Conformity assessment.
- Article 47 — EU declaration of conformity.
- Article 48 — CE marking.
- Article 49 — Registration.
- Annex VI — Conformity assessment procedure based on internal control.
- Annex VII — Conformity assessment based on quality management system and assessment of technical documentation.
- Annex I — Union harmonisation legislation.
- Annex III — High-risk AI systems.
Do you know which conformity route applies to your AI system?
Before considering a notified body, CE marking or technical documentation, the organisation must correctly determine classification, applicable procedure and required evidence.
Start the diagnostic →
Céntrika’s diagnostic can help identify that starting point.